Sury.org shipped new PHP builds for every active branch at once, landing PHP 8.6.0 as a major release alongside routine security passes for 8.5, 8.4, 8.3, and 8.2. The fixes all clear the same three session-based RCE vulnerabilities, with 8.4.28 carrying the fullest list at eleven CVEs and 8.5.13 adding one use-after-free. In a twist that trips up many admins, sury also backported today's security fixes to its long-dead branches (8.1 down to 5.6), which keep their old version numbers so php -v gives a false all-clear.
Sury.org ships PHP security updates across every branch, including dead ones; PHP 8.6.0 arrives too
The sury.org repo pushed fresh builds for both Debian and Ubuntu Linux for all active branches today, and it also backported today's fixes to its long-dead branches. There's no advisory, no bulletin, and your oldest installs won't even change version numbers.
The Debian PHP repository run by Ondřej Surý delivered a new build for literally every active branch at once. That's 8.6.0, 8.5.13, 8.4.28, 8.3.37, and 8.2.36 all going live today. The 8.6 release is the oddball. It's a brand-new major version, tagged today. The rest are the usual quarterly security pass, and they share the same three session bugs.
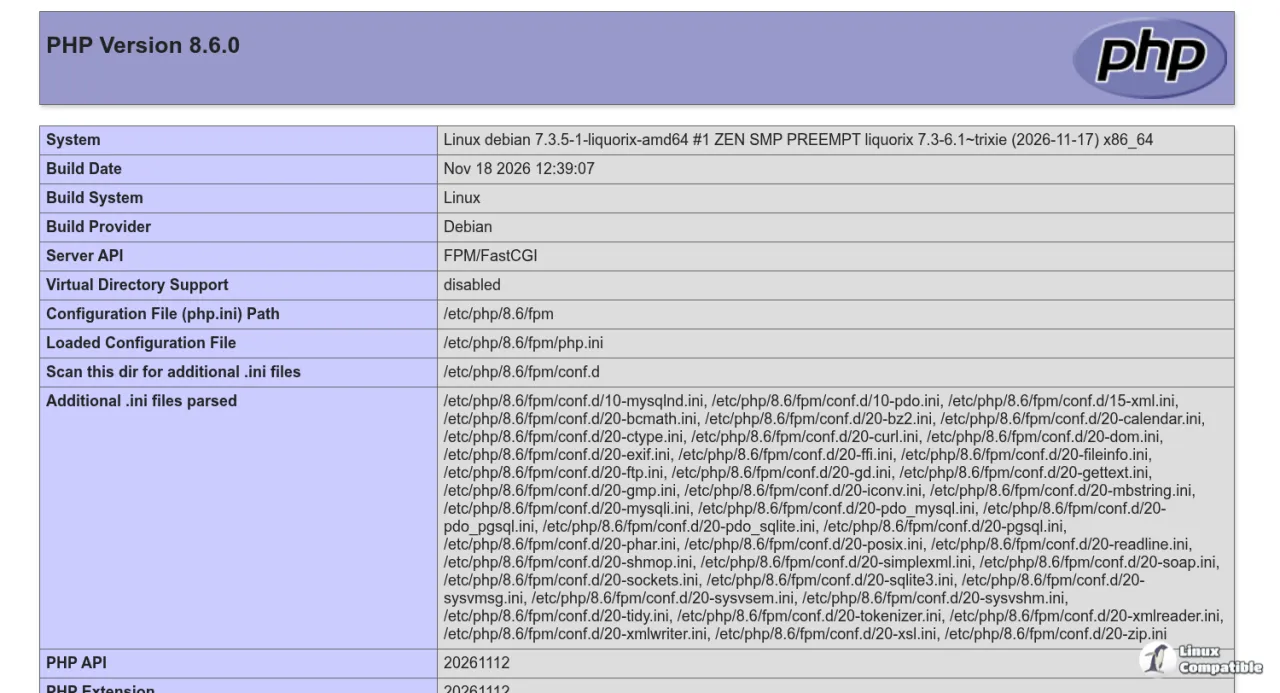
The one you'll want to care about first.
A partially overwritten session file used to be all it took to pull off remote code execution. PHP validated the entire session ID instead of stopping at the first NUL byte, and this build fixes that. That's CVE-2026-126714. The same trio also covers CVE-2026-115560, a session serializer mismatch, and CVE-2026-129481, a use-after-free triggered by an interrupted session shutdown.
8.4.28 carries the longest list, and there's a plain reason. More extensions are active in that branch, so more of them show up. Out-of-bounds reads in the CGI PATH_INFO handler. A timezone-cache use-after-free that also opens an RCE door. PHP-FPM request smuggling through an unread request body. A double free while serializing DOM XML. Eleven CVEs total.
8.5.13 adds just one: a use-after-free in magic-method backtraces, CVE-2026-129474, also an RCE.
Keep in mind that 8.3.37 and 8.2.36 share those same session fixes but their per-extension CVE lists differ slightly. Check each branch's own changelog before you roll.
If you're chasing today's full security set, target 8.5.13, 8.4.28, 8.3.37, or 8.2.36. Adopt 8.6 and you get the new features bundled with the current fixes, since that branch is newer than the bugs themselves. Either way works.
Backports keep the dead branches alive
Now the part that trips people up most.
Once PHP hits end of life, upstream stops touching it. PHP 8.1, 8.0, 7.4, 7.3, 7.2, 7.1, 7.0, and 5.6 are all dead. So why is sury still updating them?
It repackages the final upstream release against whatever the current base libraries happen to be, and slips today's security fixes into the mix. The result is a set of backports that look stale but carry the same patches. Today's builds carry these revisions:
- 8.1.34-14
- 8.0.30-31
- 7.4.33-37
- 7.3.33-41
- 7.2.34-70
- 7.1.33-85
- 5.6.40-109
How to apply it
On sury.org it's a standard apt workflow. You need a source pointing at https://packages.sury.org/php/ and the official keyring imported, which per the project's own README.txt looks like this:
# As root (or with sudo)
apt-get update
apt-get -y install lsb-release ca-certificates curl
curl -sSLo /tmp/debsuryorg-archive-keyring.deb \
    https://packages.sury.org/debsuryorg-archive-keyring.deb
dpkg -i /tmp/debsuryorg-archive-keyring.deb
sh -c 'echo "deb [signed-by=/usr/share/keyrings/debsuryorg-archive-keyring.gpg] \
    https://packages.sury.org/php/ $(lsb_release -sc) main" > \
    /etc/apt/sources.list.d/php.list'
apt-get update
Once that's in place, upgrading is a single command:
apt-get update
apt-get install --only-upgrade php            # or a specific SAPI, e.g. php-fpm, php-cli
Head here to the Sury.org website.


