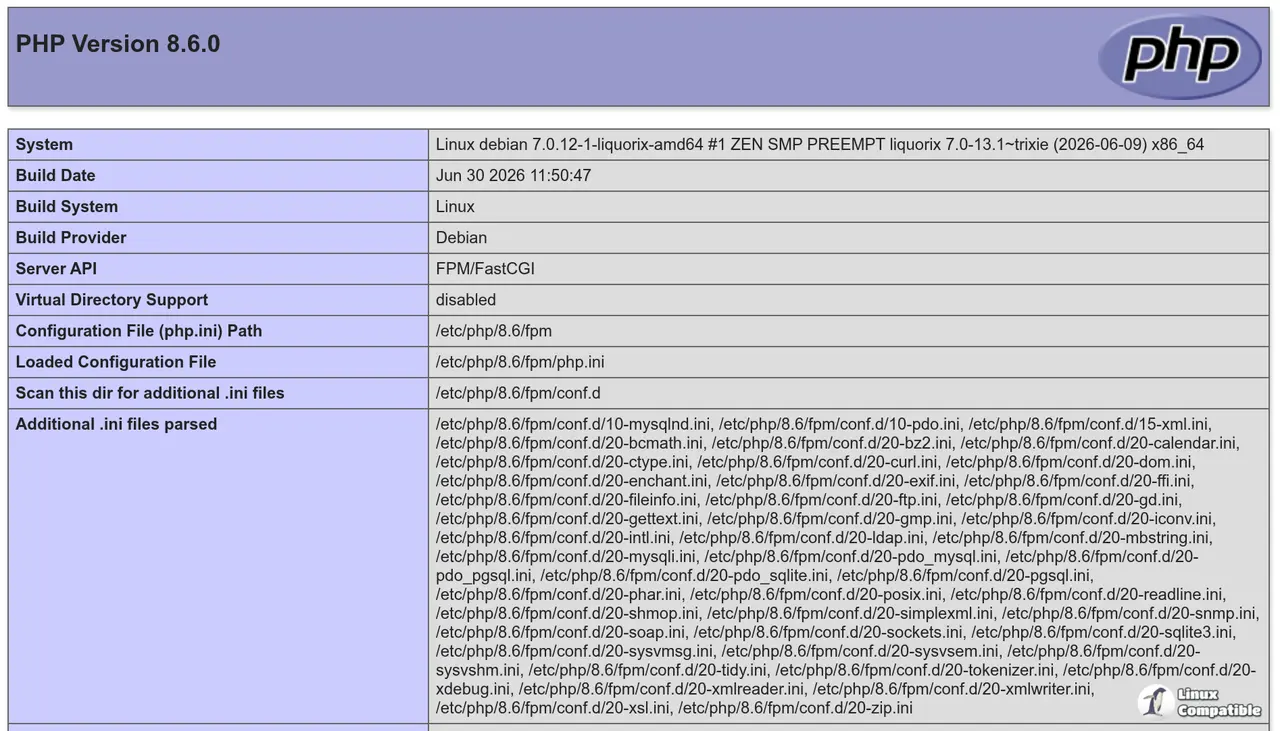
PHP 8.6.0 shipped today as a feature-heavy major release, landing the same day four older branches got an unusual all-at-once security sweep. The patch closes 12 to 17 CVEs per branch, including several network-reachable remote code executions and memory-corruption bugs in sessions, PHP-FPM and the timezone cache. Notably, today's 8.2.36 is likely one of 8.2's final releases before end of life on 31 December 2026, making an urgent migration off 8.2 advisable. Teams aiming for 8.6 should review its deprecations first, especially the removal of the mbstring regex functions.
PHP 8.6 launches today with a coordinated security sweep across every live branch
PHP 8.6.0 lands today, the same day 8.2.36, 8.3.37, 8.4.28 and 8.5.13 get an unusual all-branches security patch.
The PHP Group pulled off a two-headed release today. On one side sits 8.6.0, the feature-heavy major version the project has been chipping away at for a while. On the other, four older branches got swept up in a coordinated security patch, and this one reaches all the way down to 8.2. That branch ends support in roughly six weeks, so today's 8.2.36 is likely one of its final acts.
PHP's release calendar has become almost reliable over the past few years. A major lands around this time each autumn, and the older branches get a seasonal tune-up right beside it. Today fits the pattern, except the security team decided to knock out every live branch in one shot. PHP doesn't usually coordinate like this. You typically get a bugfix release here and a security patch there, a couple weeks apart at best.
What actually got patched
Fourteen distinct vulnerabilities appear across the shared fleet, with a handful of extras confined to the newer branches. The per-branch tally runs from 12 CVEs on 8.2.36 up to 17 on 8.5.13.
The ugliest ones are the remote code executions, and they're mostly memory-corruption bugs. Use-after-frees and double-frees nestle into session handling, the FastCGI/FPM request pipeline, and the timezone cache. Those aren't hypothetical. They sit exactly where untrusted input touches the engine core, which is precisely the spot you don't want an attacker occupying. The timezone use-after-free (CVE-2026-129496) lands in all four branches. PHP-FPM takes a double whammy: request smuggling through an unread HTTP body and an epoll use-after-free that can climb into local privilege escalation.
Not every branch gets the same slice. 8.5.13 carries the broadest fix set, including two Core use-after-frees absent from the older lines and a URI serialization hole patched alongside a bump to the bundled uriparser library, up to 1.0.3. 8.4.28 mirrors most of that, minus the Core-only holes. 8.3.37 is security-only now and trims the DOM double-free that reached 8.4 and 8.5. 8.2.36 drops both the session-shutdown use-after-free and the DOM fix, but keeps the shared FPM, Session, SOAP, Phar and Standard holes.
The short version: anything older than today's releases stays exposed until it patches, and the RCE plus memory-corruption mix is the kind of combination that turns a lazy afternoon into an incident report. Head here to the full advisory if you want to eyeball the CVE list.
PHP 8.6.0: the new, shiny thing
The major release is PHP's shorthand for "bigger changes this time," and 8.6 leans into it. Partial function lets you feed some arguments up front using ? and ... placeholders and get a Closure back out. A new \Time\Duration class handles stopwatch-style timing with nanosecond precision, and clamp() squeezes any comparable value into a range. SortDirection replaces the historical sprawl of SORT_ASC, integers, booleans and strings with a single enum.
The extension-level additions probably matter more for most shops. The new Io\Poll polling API gives event-loop libraries like ReactPHP and AMPHP a genuine replacement for the ~1024-connection ceiling of stream_select(). Streams can now throw structured exceptions instead of merely emitting warnings, and Sodium gains post-quantum key encapsulation.
It isn't all gains, though. PHP is leaning hard on deprecations this cycle, and a couple will actually bite. The mbstring regex functions (mb_ereg(), mb_split() and friends) are deprecated because Oniguruma is no longer maintained; PCRE with the u modifier is the recommended detour. Returning a value from inside a finally block is deprecated, as is returning a value from a constructor or destructor. Session defaults get tightened too: strict mode and httponly cookies switch on by default, and the cookie's SameSite moves to Lax.
Oniguruma being unmaintained is a legitimate reason to retire it, but teams still leaning on mb_ereg() should migrate before 8.6 goes live. The migration guide at php.net/manual/migration86.php lays out the rest.
Upgrade whatever you're running to today's releases, 8.5.13, 8.4.28, 8.3.37 and 8.2.36, because these patches close network-reachable RCEs. Keep in mind that 8.2.36 may well be the branch's last release before EOL, which lands on 31 December 2026. If you're still on 8.2, treat getting off it as urgent. Planning an 8.6 upgrade? Work through the deprecations and run your code against the migration guide before pushing to production.
As of right now, 8.1 sits in the unsupported zone with no patches coming, and 8.4 rolls into its own final months. PHP backs each branch for four years: two of active bugfix and security work, then two more of critical-security-only fixes before the door shuts.
Release php-8.6.0 · php/php-src
Tag for php-8.6.0
Release php-8.5.13 · php/php-src
Tag for php-8.5.13
Release php-8.4.28 · php/php-src
Tag for php-8.4.28
Release php-8.3.37 · php/php-src
Tag for php-8.3.37
Release php-8.2.36 · php/php-src
Tag for php-8.2.36


